Turn DPDP Act 2023 Compliance into Enterprise Operational Strength
From personal data discovery across ERPNext & multi-cloud databases to continuous demonstrable governance. TruSync translates India’s Digital Personal Data Protection Act requirements into automated technology controls, verified audit trails, and ERP-integrated privacy workflows.
✔ 100% Data Principal Rights
✔ Zero Data Leakage Logic
✔ ISO 27001 & SOC 2 Aligned
✔ Audit-Ready Telemetry
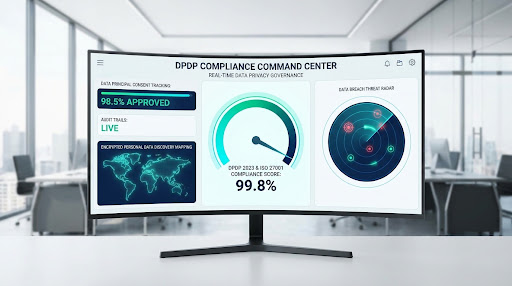
Data Discovery
14,200 DocTypes Indexed
Data Breach Radar
● Live
Who Needs to Consider DPDP Compliance?
The DPDP Act, 2023 applies to any enterprise processing digital personal data. See how TruSync operationalizes privacy governance across key industry verticals.
Manufacturing
Customer, employee, vendor, dealer, enquiry, and supply chain personal data embedded in procurement contracts and production logs.
✔ Vendor KYC Masking & NDA Vaulting
✔ Employee Biometric & HRMS Isolation
IT & SaaS Platforms
User account telemetry, multi-tenant databases, CRM customer lists, support ticket attachments, and offshore infrastructure routing.
✔ Global Data Transfer Blacklist Safeguards
✔ SDK & Analytics Cookie Consent Orchestration
Retail & E-Commerce
Order histories, shipping addresses, phone numbers, payment tokens, loyalty card records, and personalized marketing automation databases.
✔ Instant 1-Click Marketing Consent Opt-out
✔ Right to Erasure across Delivery 3PLs
Banking & NBFCs
Customer KYC records, Aadhaar numbers, loan disbursements, bureau scoring telemetry, transaction ledgers, and wealth portfolios.
✔ 7-Year RBI Retention vs. Erasure Harmonization
✔ Mandatory DPIA & Independent Privacy Auditing
Healthcare & Diagnostics
Patient electronic health records (EHR), lab diagnostic data, doctor appointments, telemedicine call logs, and pharmacy order flows.
✔ Medical Purpose-Limitation Enforcements
✔ Granular Doctor-Patient Consent Tokens
Real Estate & Hospitality
Buyer deed agreements, tenant verification files, hotel booking records, passport/ID scans, and onsite visitor management logs.
✔ Front-Desk Identity Redaction Engine
✔ Automated Check-out Retention Deletion
12 Key Pillars of DPDP Compliance
India’s DPDP Act, 2023 mandates actionable operational controls across every stage of the personal data lifecycle.
Data Discovery & Inventory
Automated deep-scanning across ERPNext, MariaDB, S3 buckets, and legacy silos to classify personal data assets and establish live data flows.
Purpose & Lawful Basis
Strict mapping of every DocType and processing transaction against legitimate business purposes or explicit consent bases under Section 4.
Privacy Notices
Multilingual, transparent privacy notices formatted in clear plain language with itemized disclosures on data items and redressal channels.
Consent Management
End-to-end consent lifecycle: unbundled affirmative opt-ins, cryptographically verified consent tokens, and instant right to withdraw.
Data Principal Rights
Self-service user portals powering instant right to access summary, correction, update, nomination, and grievance redressal resolution.
Security & Encryption
Mandatory technical safeguards: column-level AES-256 database encryption, role-based field masking, and zero-trust access logging.
Breach Management
Immediate anomaly detection, structured impact escalation, and automated incident dossiers for mandatory Data Protection Board reporting.
Retention & Erasure
Automated database cron jobs that purge or anonymize personal data once specified transaction purposes expire or consent is revoked.
Processor Governance
Enforceable data processor contracts, third-party sub-processor registries, automated API scopes, and periodic external vendor audits.
DPIA & Risk Assessment
Pre-deployment Data Protection Impact Assessments (DPIA) integrated into software release pipelines and corporate change-management.
Children & Guardians
Strict ban on behavioral tracking and targeted ads for minors. Verifiable parental consent verification mechanisms built directly into apps.
Demonstrable Audit Trails
Immutable, timestamped system logs detailing who processed what data, when, under which consent ID, ready for regulatory inspection.
Bridge Legal Mandates with Operational IT Systems
Conventional compliance solutions rely on static spreadsheets. Sentinel-DPDP is an active, deterministic privacy control suite that hooks natively into your ERP, CRM, and databases.
◆ Automated DocType Discovery Engine
Continuously scans Frappe & ERPNext schemas to catalog personal identifiers, PII fields, and third-party data exchange points.
◆ Unified Consent Management API
Provides lightweight REST/GraphQL endpoints for web forms and mobile apps to register, version-control, and log user consents in real-time.
◆ Right-to-Erasure Workflow Automator
Orchestrates complete cascade deletions across ERP sales orders, logs, and CRM records while preserving statutory accounting records.

● STATUS: DEMONSTRABLE AUDIT LOG ACTIVE
The 6-Stage DPDP Implementation Lifecycle
We move organizations from abstract legal compliance checklists to an automated, operational privacy framework integrated into enterprise daily workflows.
01
DISCOVERY PHASEAssess
Understand your personal data perimeter, legacy databases, DocType structures, vendor exposure, and identify immediate compliance gaps.
02
ARCHITECTUREDesign
Draft customized privacy policies, granular consent schemas, field-level access control hierarchies, and DPIA risk evaluation blueprints.
03
DEPLOYMENTImplement
Deploy dynamic multilingual notices, consent token APIs, AES-256 database column encryption, and self-service grievance redressal portals.
04
ERP INTEGRATIONIntegrate
Connect Sentinel-DPDP bi-directionally with your ERPNext, Frappe LMS, HRMS, CRM, website lead forms, and mobile application backends.
05
CONTINUOUS OPSMonitor
Real-time compliance telemetry, SLA tracking for Data Principal erasure/access requests, vendor access auditing, and automated threat scans.
06
VERIFICATIONDemonstrate
One-click generation of immutable audit evidence, compliance scoring sheets, and regulatory submission packages for the Data Protection Board.
Schedule Your DPDP Readiness Discovery Session
Not sure where your organization stands regarding the DPDP Act 2023 and upcoming 2025 Rules? Our certified enterprise consultants review your systems, DocTypes, and current consent workflows to pinpoint high-risk vulnerabilities.
Frappe Certified Partner
Native ERPNext codebase architecture and module auditing.
ISO 27001 & SOC 2 Aligned
Audited security protocols ensuring your data remains isolated.
Strict Mutual NDA Guaranteed
All architecture reviews are conducted under binding confidentiality.
Direct Enterprise Desk:
[email protected] • +91 81434 83438
Request DPDP Readiness Review
Share your details — a senior DPDP technology consultant responds within 24 hours.
By submitting, you agree to TruSync's privacy policy. Your information is securely handled under mutual non-disclosure.